Crypto AML compliance services: policy building, risk assessment, and programme reviews for your business
Published: Last reviewed: How we edit
A crypto business needs an AML programme built around its own risks. That means a written risk assessment, clear policies, checks on customers, screening, monitoring, records and training. We coordinate independent specialists in compliance who help you build that programme or review the one you have. To be plain about our role: we are not a regulated auditor, not someone licensed as a money laundering reporting officer, and not a law firm. What a regulator or bank decides is the part we cannot promise.
Not sure what to do next? Write to us:
Everyday situations
- A bank or a payment provider has asked to see your AML policy, your risk assessment and a plain description of your controls
- You shipped something new, like staking, a fresh token listing or a new country, and the old risk assessment no longer matches reality
- Bringing customers on takes too long, or goes differently each time, because the KYC steps are not written down clearly
- Screening and monitoring tools keep raising alerts, but there are no written rules for how your team should handle them
- A regulator or an auditor has raised findings, and you need a workable plan to respond to each one
- Your policy started life as a template, and nobody has checked whether it actually matches what your business does
- A new compliance officer has just joined the team and needs a structured handover of everything
This fits if you
- Founders of a crypto start-up who need AML policies in place before speaking with a regulator, a bank or a payment partner
- Compliance officers who would like another set of eyes on their policy set or risk assessment
- You are the finance or operations lead. A bank or payment partner asked you for AML documents.
- Teams that scaled quickly and still run on copied templates that no longer fit what they actually do
- Business owners getting ready for an audit, a partner's review, or questions from a regulator
How the case runs
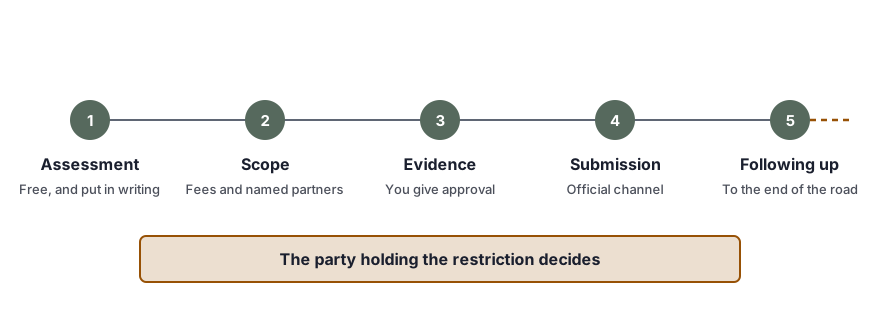
- No-cost evaluation
Tell us what the business does, who is asking for what, and why. We answer in writing: whether independent compliance specialists can help you, and what they would need to look at.
- Scope and fee in writing
Before any payment, you get everything in writing: the scope, the proposed specialists, the deliverables and the fee model. Together we set what is in scope and what is not.
- Learning the facts
Next, specialists go through your paperwork and talk with your team. You will get a list of questions and a date to answer them by.
- Documents we draft
The specialists prepare drafts, either documents or a gap report. We review each one for plain wording and a good fit with your facts, then walk your team through what they say.
- Passing things on
You receive the final versions, an action list with owners, and a short note on what is still open. One thing does not change: your named compliance officer keeps ownership of the programme.
What we do
- See how your business works and where the risks sit
First, we look at what you actually run: your products, your customers, the countries you serve, how money moves, and the technology behind it. A short fact sheet plus a few interviews show the independent specialists which risks really apply to you. That way the programme is built around your business, not copied from a generic template.
- Write or review the risk assessment
Compliance specialists work with you to build a firm-wide risk assessment: they rate your customer, product, geographic and delivery risks, and connect every rating to a control. Where a control already exists, they check it for gaps, outdated assumptions and missing evidence.
- Check policies against daily practice
Together we look at your written rules for onboarding, screening, monitoring, record keeping and escalation, then at what your team really does each day. You receive the gaps in plain words, plus a list of next steps. Which legal rules apply to you is something your lawyer confirms.
- Help you pick tools
First we draft the requirements your KYC, sanctions screening, blockchain analytics and case management tools should meet. Next we line up the options against those requirements and plan a trial. For now, the buying decision and the contract stay in your hands.
- Get your team and your answers ready
We write short briefings for staff, and a list of questions a bank, an auditor or a supervisor is likely to raise. Alongside each question goes a draft answer, built only from your own documents. Every answer stays yours.
What to have ready
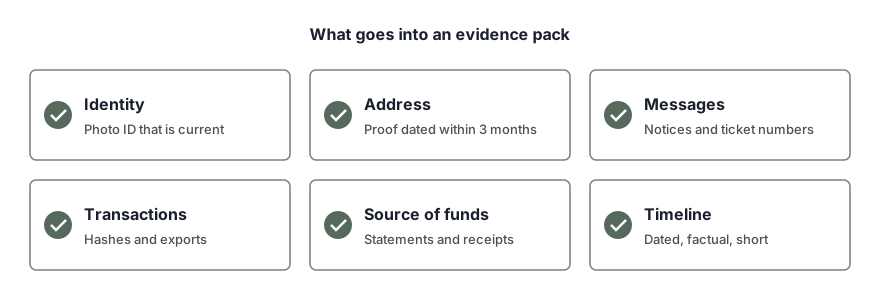
- A short plain summary of your products, services, customer types and the countries you serve
- Your current AML, KYC, sanctions and monitoring policies, drafts included
- Your most recent risk assessment, if you have one, plus the date it was last refreshed
- A chart of your organisation showing which people fill compliance, management and board seats
- Onboarding forms and alert examples, with all personal data stripped out
- The KYC, screening and analytics vendors you rely on, plus what each one does
- Any documents you receive from a regulator, bank, or payment partner.
- Your license or registration numbers, if you have them
What we cannot do
- We guide you, but we are not a regulated auditor, a licensed reporting officer, or a law firm. We do not offer legal advice or certify compliance.
- We are not your compliance officer. We do not decide on your customers or file reports with any authority. Those duties remain yours.
- Regulators, banks and auditors make up their own minds. We cannot make them accept your documents or reach a particular view, and no licence, account or approval is promised here.
- A review we coordinate is advisory only. It does not replace an independent audit or any legally required review by a qualified party.
- We do not ask for your seed phrase, private keys, or passwords. No one on our team needs access to your wallets or funds.
Questions people ask
When a crypto business puts together an AML programme, what does it usually cover?
In most cases: a risk assessment covering the whole business, written policies, customer due diligence, screening for sanctions and addresses, transaction monitoring, record keeping, staff training, and one named person who carries the responsibility. The details follow from your products, your customers, and the rules that apply to you. Your lawyer confirms which rules those are.
Could you serve as our compliance officer or MLRO?
No, and we want to be plain about this: we are not a licensed officer, and we never step into that role. Your company keeps its own named compliance officer. That person stays in charge of decisions and filings. Independent specialists can back them up with reviews, drafts and training, but the responsibility stays inside your business where it belongs.
Do you commit to us clearing a regulator's review?
No. Regulators, banks, and auditors make up their own minds. What we can do is help you put clear, consistent documents in front of them and get ready for the questions they are likely to ask. We cannot promise approval, or any particular outcome.
Which rules apply to my business?
Several things shape this: where you do business, what services you provide, and who your customers are. We cannot advise you on the law here. Your lawyer, or the supervisor's published guidance, is what settles the rules. After that, our specialists line your paperwork up against the list you hand them.
How do we know the difference between a program and a simple template?
A template only offers some headings. A full program must include a risk assessment of your specific products and clients. It requires records showing controls that your staff actually use. We review all your paperwork against your business operations.
Does working with us mean sharing all of our customer data?
Not immediately. Our specialists start with policies and process descriptions, using samples with personal information removed. Should the review require actual records, we must agree on this in writing first. Access will be strictly limited to what the current task needs.
How long it takes
How long it takes depends on how big the business is, how many products it has, and how fast your team gets back to us with answers. A focused review is quicker than a full set of policies. We set the dates in the written scope, and if something slips, we tell you early.
Fees
The first assessment costs nothing. If we go ahead, you get a written quote for the scope and the fee model, with the independent specialists' fees listed on their own line. Nothing gets charged until we have told you whether we can help and you have accepted the scope. Fees →
Related situations
- Due diligence and risk checks for crypto firms. Evidence-based written checks on customers, counterparties and wallets, each with a clear risk rating.
- Crypto transaction monitoring advice for firms. Set up scenarios, thresholds and alert steps for on-chain and off-chain activity.
- Reading a blockchain analytics report. A traced source-of-funds report, written for a compliance team to use.
- Disputing wallet risk flags and screening results. Flagged as high risk by a screening tool: trace the funds and dispute the label.
Read next
Sources
These are the official or authoritative pages behind this page. Sources get updated over time, so check them for the current wording.
- Application of FinCEN's Regulations to Certain Business Models Involving Convertible Virtual Currencies (FIN-2019-G001) · Financial Crimes Enforcement Network (FinCEN)
- Cryptoassets: AML / CTF regime · Financial Conduct Authority
- Guidelines amending the ML/TF Risk Factors Guidelines (EBA/GL/2024/01) · European Banking Authority
This page gives general information only. It is not legal advice.